Work toward ISO 27001 one clear step at a time
A guided workspace for Swedish and European companies building their information security management system. It shows what to do next, explains why the auditor asks, and runs in your own instance in the EU.
-
Set direction
- Context and scope4.1–4.3
- Objectives and roles5.3, 6.2
- Risk assessment6.1.2
-
Put it to work
- Statement of Applicability6.1.3
- Policies and controlsAnnex A
- Evidence that it runs7.5, 8
-
Check and prepare
- Internal audit9.2
- Management review9.3
- Ready for Stage 1 and Stage 2 with your certification body
What you work with every week
Built on CISO Assistant, the open-source GRC platform, with a Hisland layer that decides the order and keeps the language plain.
Start from your company, not a blank framework
Five short questions about who you are, why now, your scope, where you stand and your yearly rhythm. Your answers switch on the modules you need, apply the Hisland ISO 27001 journey and put the big dates in the calendar.
How the starting point works- Your companySize, sector, who runs IT, where data lives
- Why nowCustomer demand, a tender, NIS2, insurance
- ScopeSites, systems and people, in one sentence
- Where you arePick the sentence that sounds like you
- Your rhythmReviews, internal audit, target quarter
Then one action: set up my workspace.
Every step says why the auditor asks
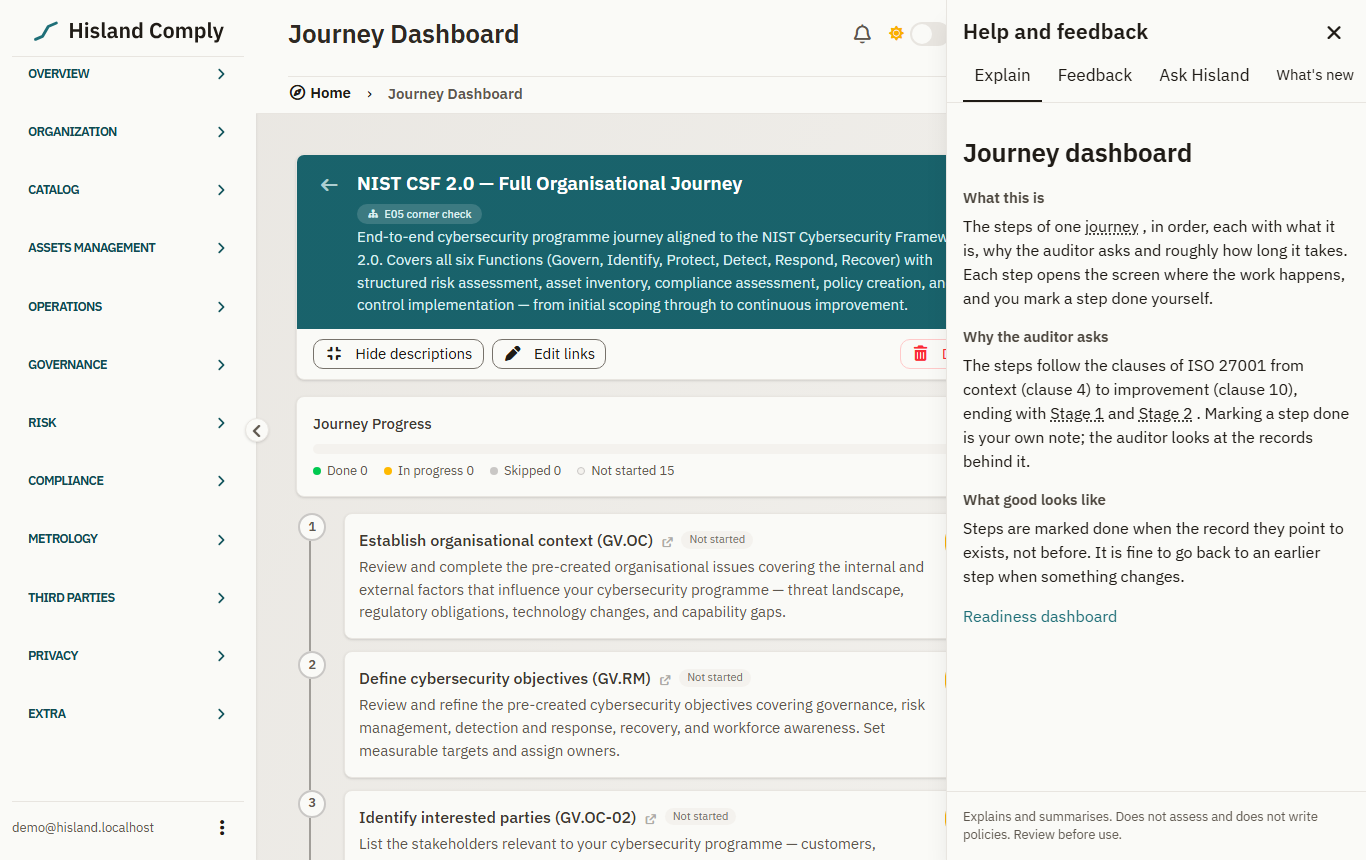
The Hisland ISO 27001 journey follows the standard from context to improvement. Each step opens the screen where the work happens, tells you roughly how long it takes, and what good looks like. You mark a step done when the record it points to exists.
Readiness you can act on, without a score
One page shows what would stop a Stage 1 audit, what could go wrong at Stage 2, whether the two hard gates are done, and how much is documented compared with what is actually operating. Counts and dates, never a single percentage.
A person to ask when the standard gets vague
The help corner sits on every screen. Read a plain explanation of the page, send feedback, or ask a Hisland consultant. Your question arrives with the step you were on, so nobody has to start from the beginning.
Working with a Hisland consultantYour own instance, in the EU
No shared database with other customers. The code underneath is open source, so you can see what runs and take your data with you.
One instance per customer
Your workspace runs on its own, with its own database and backups.
Hosted in the EU
Application and data stay in [provider, region].
Open source base
CISO Assistant Community by intuitem, AGPL. The Hisland layer is public too.
AI is optional
When switched on, it runs on an EU endpoint in Paris and only explains and summarises.
For companies doing this for the first time
Small and mid-sized companies without a full-time security team, where someone has been asked to get ISO 27001 in place and wants a clear path rather than a blank register.
- A customer asks for itSecurity questionnaires and contract clauses
- A tender requires itPublic and private procurement
- NIS2 applies to youDirectly, or through your customers
- Insurance wants evidenceCyber insurance renewals
Questions people ask first
Does Hisland Comply certify us?
How is this different from Vanta or Drata?
Which frameworks are covered?
Is it available in Swedish?
Want to see it with your own scope?
A short call where we walk through the starting point using your company as the example.